Web
We test business logic: prices, coupons, permissions and sessions. The things a scanner doesn’t understand.
See serviceWeb, API and mobile pentesting under written authorisation. Every finding comes with the full path: how we got in, what we reached and what to fix first.
We build the team around what needs testing: web, mobile or infrastructure. A person confirms every finding before it reaches your report.
OWASP ASVS · PTES · NIST SP 800-115
A report and attestation letter your auditors and customers accept for SOC 2, ISO 27001 and vendor security reviews.
Breach Path links findings into routes: where someone gets in, what they reach and which step breaks the chain. Try the demo.
staging.acme.example, no owner.
reachable without VPN.
never changed after deploy.
full export possible.
Take staging.acme.example off the internet and rotate the default credentials.
linked from their profile.
old commit, never rotated.
backup bucket.
Revoke the leaked token and purge the secret from the repo history.
from an unrelated service.
same password, no second factor.
from outside, as an employee.
Force a reset on the reused passwords and require a second factor on remote access.
We set the scope with you. Every finding is reproducible, and once you fix it we test it again.
We test business logic: prices, coupons, permissions and sessions. The things a scanner doesn’t understand.
See serviceWe change one number in the request and see whether the API hands over another customer’s data.
EnquireWe intercept your Android and iOS app traffic, bypass pinning and check what it stores on the device.
See serviceThick clients: DLLs loaded from the wrong place, passwords inside the installer and unencrypted traffic.
EnquireFrom a crash to control of the program: overflows, ROP and how DEP and ASLR get bypassed in your software.
EnquirePrompt injection, data leaks and agents that do more than they should.
EnquireFrom an unprivileged user to Domain Admin, with every step of the path documented.
EnquireOpen buckets, keys left in repositories and roles with more permissions than they need.
EnquireYour perimeter changes every week. We watch it and tell you what’s new before someone else finds it.
See the modeWe publish browser and mobile security research, with the methodology and evidence so anyone can check it.
Explore researchA 30, 60 or 90-day window: we watch what changes on your perimeter and tell you before someone else takes advantage of it.
We map your external surface and set the starting point. You know exactly what you expose today.
We compare against the baseline and show you what is new, what reopened and what is already fixed.
We retest earlier findings and only close the ones we confirm are fixed.
In both modes, a person validates every finding.
AI to correlate information and prioritise review. Our hackers test and validate every finding.
Reconnaissance, testing and analysis without AI models. For projects that need to exclude AI throughout the engagement.
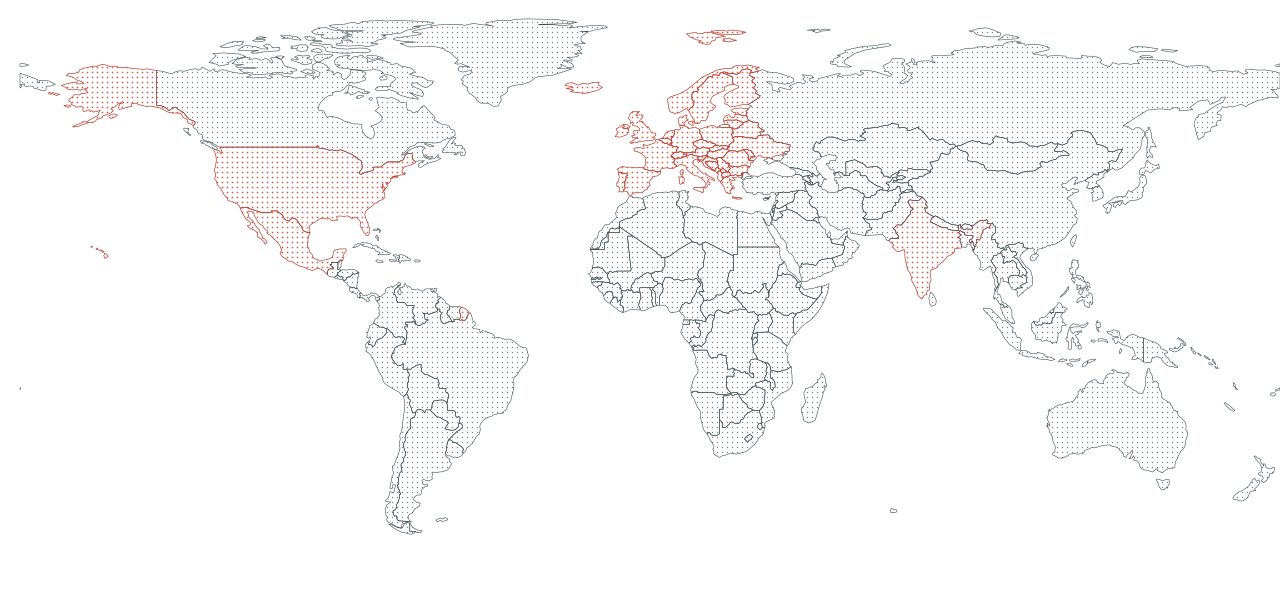
All remote: Mexico, the United States, Europe and India.
We reply with a proposed scope and working mode.
We reply with a proposed scope and working mode.
sales@knullcorp.comFindings with evidence, impact, reproduction steps and prioritised fixes. Includes retesting and a session with your team.
We agree on assets, testing windows, data handling and a technical contact. Testing starts with written authorisation.
Yes. We sign a confidentiality agreement before exchanging sensitive technical information.